
be.OT Secure Industrial Platform
European OT cybersecurity platform embedded in its own network, to protect critical infrastructure such as power grids, water supply, and industrial environments end to end
Security that lives inside the OT network
- Security built into the routers and gateways that already carry OT traffic
- More than 1,000 industrial protocol signatures, such as IEC 60870-5-104, IEC 61850, and DNP3
- Passive asset inventory and a single management console for the entire OT network
- Centralized, distributed, or hybrid deployment, according to the needs of each location
- European manufacturer whose equipment helps meet NIS2, CRA, and IEC 62443 compliance
Critical infrastructure under attack

Critical infrastructure, from power grids to water supply and industrial plants, is no longer a theoretical target. In late December 2025, Poland foiled an attack against cogeneration plants and management systems for wind and solar farms, which its government linked to Russian services. In July 2026, attackers exploited internet-connected PLCs across more than 30 water systems in Minnesota (U.S.), locking some operators out and forcing equipment to be operated manually. In October 2026, a wave of attacks raised refrigerator temperatures at hundreds of supermarkets in France and, in early November, in Belgium and other European countries, with product losses valued in the millions of euros.
On top of this comes growing regulatory pressure. The NIS2 Directive requires essential entities, among them those in the energy sector, to manage their cybersecurity risks, and the Cyber Resilience Act (CRA) requires security by design from manufacturers, with vulnerability reporting in force since September 2026 and full application in December 2027.
At the same time, the shutdown of 2G and 3G networks, primarily in Europe but also in other parts of the world, forces the replacement of many devices deployed in the field. This is the opportunity to build in security from day one, rather than adding it afterward as a separate layer.
What are the important points related to be.OT

Security inside the network
Protection is built into the industrial gateways and edge devices that carry the traffic, instead of being added as a separate layer that must be deployed, cabled, and maintained at every site.

Designed specifically for OT environments
Inspection and control purpose-built for industrial environments, with more than 1,000 OT protocol signatures, such as IEC 60870-5-104, IEC 61850, DNP3, and Modbus, and easy customization of the customer’s proprietary protocols.

Compliance by design
Supports the requirements of NIS2, CRA, and IEC 62443, with events and traceability that ease audits, and is backed by a European manufacturer with control over its supply chain and firmware.

Operation at scale
Zero-touch provisioning to deploy and maintain large fleets of devices across thousands of dispersed locations, with a consistent security policy, no configuration drift, and no unnecessary site visits.
OT cybersecurity: protecting without disrupting
Several factors make this environment unique. Assets are distributed across plants, remote stations, or isolated equipment, with variable connectivity. Equipment and platforms from different manufacturers coexist, many designed to last for decades. Remote access by suppliers and engineers is necessary, but must be done with control and traceability. And communications use numerous industrial protocols, such as Modbus, DNP3, IEC 60870-5-104, IEC 61850, and OPC UA, which require specific inspection that conventional IT firewalls do not understand.
On top of this is a visibility problem: you cannot protect what you cannot see. Unknown or unauthorized devices are a threat, and telling normal behavior from anomalous behavior in machine-to-machine flows requires an approach centered on OT protocols, with specific detection, passive inventory, and progressive response.
That is why OT cybersecurity rests on three ideas:
- Protection at the edge: inspecting and controlling traffic where it originates, even when the link to the control center fails.
- Zero-trust access with industrial protocol awareness: each user or supplier reaches only the asset they need, and every session is inspected, not just authenticated.
- Unified visibility: seeing the inventory, flows, and alarms across the entire network, from the plant floor to the corporate network, in a single console.

All of this must cover every layer of the network, from the level 0 sensors and actuators to the level 5 corporate network, and do so while complying with an increasingly demanding regulatory framework, with NIS2, the CRA, and the IEC 62443 standard as references.
The Teldat be.OT Solution: the secure industrial platform
be.OT Secure Industrial Platform is Teldat’s proposal for protecting industrial and critical-infrastructure networks. It is not a single device but an OT cybersecurity architecture that brings together the protection of be.Safe Pro and the visibility of be.Safe XDR under one umbrella, with protection distributed across every point of the network and managed from a single platform with centralized control and visibility.
be.Safe PRO is the platform’s protection layer. It brings together next-generation firewalls (NGFW/UTM), intrusion prevention and detection (IPS/IDS), application control, and segmentation. It includes more than 1,000 signatures and controls for industrial protocols and makes it easy to customize the customer’s proprietary protocols.
Policies are defined once and applied consistently across all sites, with no configuration drift. OT protocol inspection and segmentation between devices run close to where the traffic originates, with low latency and without depending on the link to the control center. In addition, events are logged and traceable, which eases NIS2 and IEC 62443 audits.


The platform adds Zero-Trust Access (ZTNA) with OT protocol awareness: each engineer or supplier reaches only the industrial asset they need, and every session is inspected, not just authenticated.
be.Safe XDR is the visibility and audit layer. A passive probe, with one-way data flow, automatically discovers connected assets (IP and MAC, name, manufacturer, operating system and version, protocols, asset type, and first and last seen), without adding load or risk to production systems and without packets leaving the customer’s premises. It also shows machine-to-machine flows, detects protocols and anomalies, and generates reports and alarms, all in a single console spanning from the plant floor (level 0) to the corporate network (level 5).
Both layers can be deployed centrally, distributed, or hybrid. With hybrid SASE, the customer decides whether functions run on premises or in the cloud, and keeps a single policy across both modes.
These functions reach the network through Teldat’s industrial equipment, such as the Regesta Smart v2 (Secure Industrial Gateway) and Imber (Secure M2M Shield) families.
be.OT – Use Cases
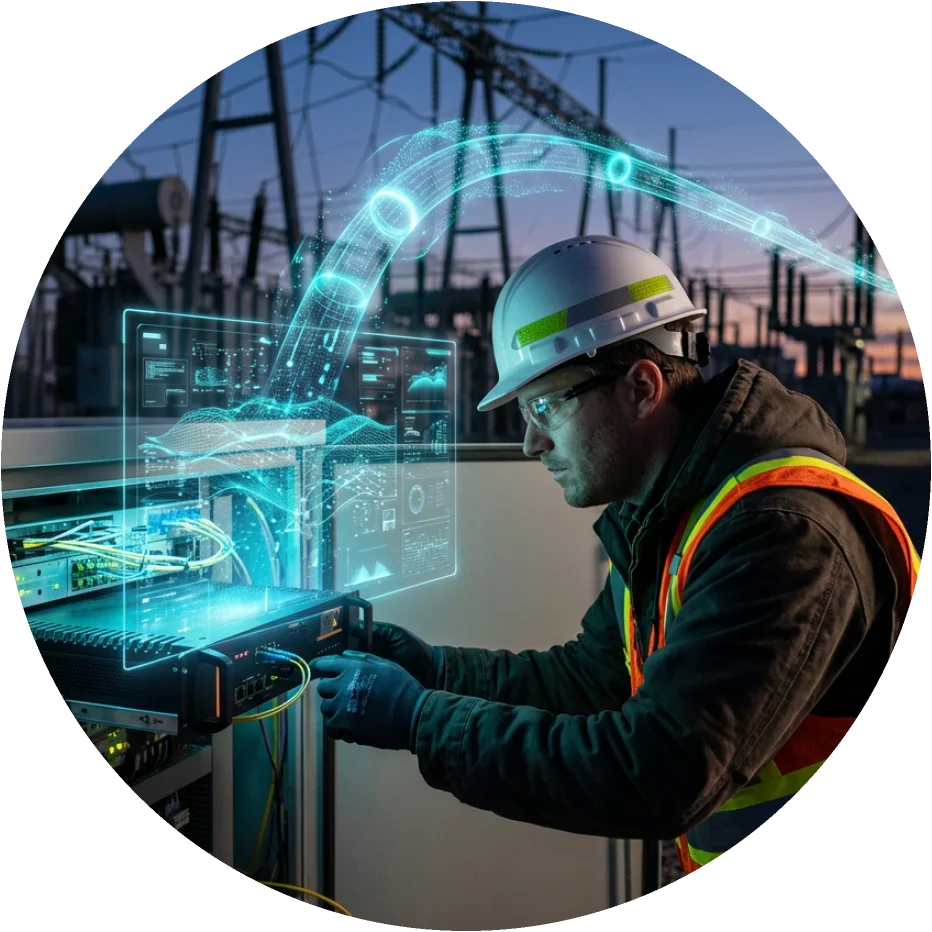
Substations and power grids
Secure connectivity between substations, RTUs, PLCs, and smart meters, and the control center, with cybersecurity built into the equipment itself.
Industrial M2M communications
Protection of sensors, robots, RTUs, and connected machines at remote locations, with secure tunnels to the corporate data center.
Smart cities
Traffic lights, streetlights, water, video, and municipal services protected end to end and managed from a single control center.
Substations and power grids
Secure connectivity between substations, RTUs, PLCs, and smart meters, and the control center, with cybersecurity built into the equipment itself.
Challenge
In addition, many of its devices still rely on 2G and 3G networks that operators are shutting down, and there is rarely an up-to-date inventory of what is actually connected at each substation. Any security measure must reinforce operational continuity, not degrade it, and the equipment must run for a decade or more with minimal maintenance.
Solution

With the Custos family of Industrial Edge devices, inspection of protocols such as IEC 60870-5-104 and the inventory run locally at the edge and keep working even if the link goes down.
Connectivity is flexible: 5G, LTE, 450 MHz, satellite networks, PRIME PLC, and BPL. Everything is managed from a single console, with zero-touch provisioning to deploy and maintain fleets of thousands of devices.
Why Teldat?
Industrial M2M communications
Protection of sensors, robots, RTUs, and connected machines at remote locations, with secure tunnels to the corporate data center.
Challenge
Many of these devices are left exposed or with weak credentials, and real incidents prove it. In 2026, internet-exposed PLCs were exploited across more than 30 water systems in the United States, and in 2025 a weak password made it possible to manipulate a valve for four hours.
Companies need controlled remote access for their suppliers, to know which devices are at each site, and to do so without adding complexity or jeopardizing operational continuity. Small teams cannot afford a different security tool for every site.
Solution

Third-party remote access follows the zero-trust model: each engineer reaches only the asset they need, and the session is inspected at the industrial protocol level. Signatures and security updates arrive automatically from the cloud. The result is a consistent policy across all sites and a single console.
Why Teldat?
Smart cities
Traffic lights, streetlights, water, video, and municipal services protected end to end and managed from a single control center.
Challenge
In 2023, a cyberattack on the traffic management system of Olsztyn (Poland) disrupted the traffic lights at nearly 100 intersections for several weeks, unauthorized radio commands brought about 20 trains to a standstill, and that same year a group compromised pressure-monitoring equipment at a municipal water utility in Pennsylvania.
City councils, with small technical teams, must protect infrastructure scattered across blocks or districts, know what is connected, and comply with NIS2 without multiplying cost or operational complexity. In addition, each service usually depends on a different supplier, which makes a single view harder to achieve.
Solution

In a centralized architecture, inspection runs on shared security instances. In a distributed architecture, each device applies the policy locally, with segmentation and zero trust between devices, and keeps protecting even if the link goes down. SD-WAN controllers maintain a single policy, and the two modes can be combined within the same city.
Why Teldat?
Read our latest Blog Posts
Understanding the technology behind heat pipes
Heat pipes transfer heat on electronic devices & industrial applications, using the heat transition principle, to transfer to heat sinks within a cooling system. Heat pipes have clear advantages over other heat dissipation methods. What are heat pipes? Heat pipes...
The importance of sequencing power domains in electronics
There is a clear trend in the electronics industry for integration, allowing for more compact and efficient designs. More and more, electronics manufacturers are making their chips smaller, including more components within their chips and extending the feature range....
Improving device reliability and redundancy
In a previous article we looked at how to mathematically calculate the reliability of electronic equipment. That is, the probability of it working correctly for a given period of time. This is best characterised by the Mean Time Between Failure (MTBF), or its...

